SEC & FINRA Compliant Documentation
Transform financial meetings into compliant documentation with automated record-keeping and complete data sovereignty. Perfect for financial advisors and wealth managers.
Regulatory Compliance
An architecture built to support SEC Rule 17a-4, FINRA record-keeping, and other financial regulations. Enterprise adds automatic audit trails and retention policies on your own infrastructure.
Financial Privacy
Bank-grade security with AES-256 encryption at rest and in transit. Zero-knowledge architecture ensures complete client confidentiality protection.
Financial Intelligence
Summary templates you can shape around financial terminology and investment discussions. Pro adds speaker identification, so board minutes and client calls capture who said what.
Trusted by Financial Professionals
Join financial advisors who protect client confidentiality with Meetily
How Meetily Compares for Financial Services
Five dimensions that compliance and IT teams ask about during procurement.
| Dimension | Meetily | Cloud bot tools (Otter, Fireflies) |
|---|---|---|
| Compliance frameworks supported | SEC 17a-4 / FINRA 4511 / MiFID II (artifact level) | Vendor-managed |
| Audit logging | Local + Enterprise admin dashboard | Vendor-controlled |
| On-device processing | 100% for transcription | Cloud-only |
| Bot in client call | No (system audio) | Yes (third-party participant) |
Compliance is implemented by the firm's record-keeping policy and storage layer. Meetily provides audit-grade source artifacts; we do not claim independent SEC, FINRA, or SOC 2 certification. Sources: SEC Rule 17a-4(f), FINRA Rule 4511, MiFID II Article 16(7).
How It Works
From client meetings to compliant documentation in three simple steps
1. Record Meeting
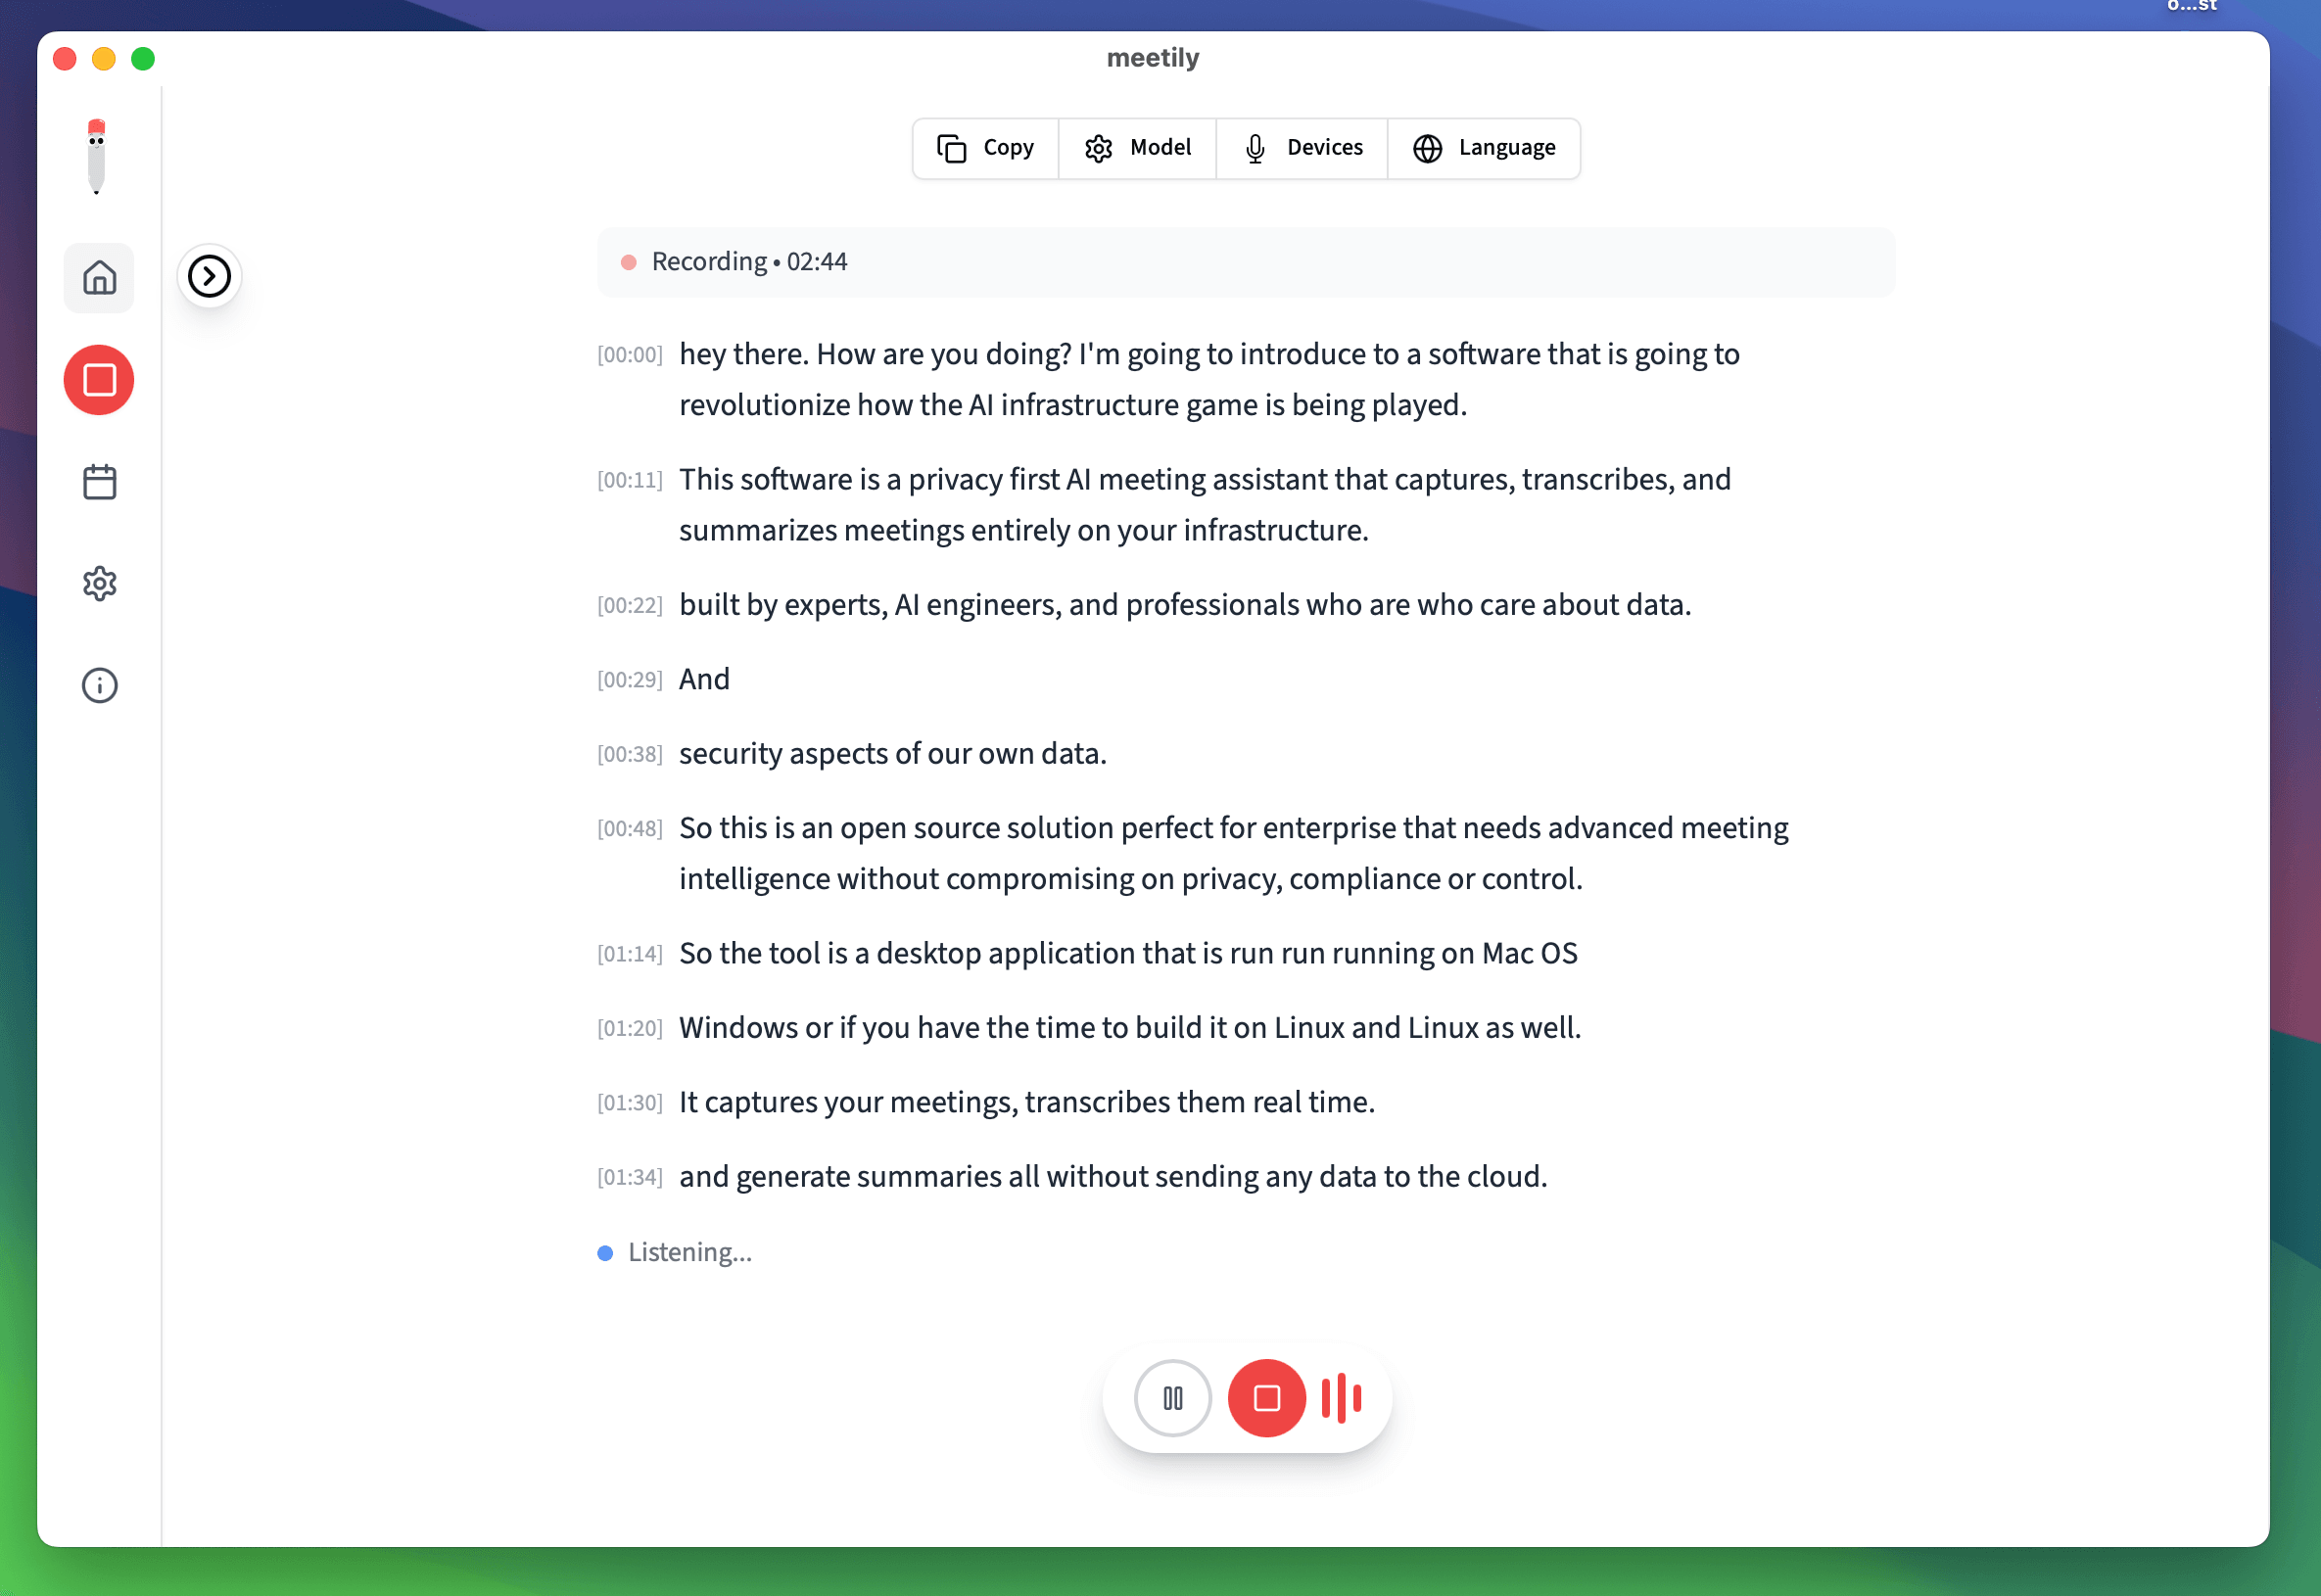
Meetily securely records your client meetings and transcribes discussions in real-time.
2. Local Processing
AI processes everything locally, ensuring complete SEC & FINRA compliance.
3. Compliant Documentation
Structured documentation is created with financial terminology recognition and compliance checks.
Choose Your Plan
From individual advisors to enterprise financial teams
Try Pro for free
Full Pro access on the advisor's device. Client conversations stay on-prem. No card required.
- Local transcription — keeps client data inside the firm
- Custom summary templates (board minutes, compliance review, client memos)
- Audit-friendly local recording retention
- Recordings saved locally — no cloud transcripts
- Advanced exports for case files and audit packs
Pro
Speaker identification and compliance features for financial professionals.
- Real-time transcription
- AI-powered summaries
- Advanced Export Options (PDF, DOCX, Markdown)
- Recordings saved locally
- Custom summary templates
- Auto-detect and join meetings
- Chat with your meetings*
- Speaker identification
- Calendar integration*
Enterprise
SEC & FINRA compliant self-hosted deployment for financial institutions.
- Everything in Pro
- Self-hosted deployment
- Admin dashboard
- Team management & analytics
- Custom compliance frameworks
- White-glove deployment
- Priority 24/7 support
- Custom integrations
Frequently Asked Questions
Common questions about Meetily's SEC & FINRA compliance, financial data protection, and regulatory features
Related Reading for Financial Services
Compliance frameworks, GDPR alignment, and self-hosted options for regulated firms.
Security & Privacy Architecture
How Meetily aligns with SOC 2 controls, encryption, and audit logging for financial firms.
Enterprise Self-Hosted Deployment
Admin audit logs and managed compliance for institutional rollouts.
GDPR Compliance Guide
Practical setup for European advisors covering MiFID II call recording and RGPD requirements.
Best Self-Hosted Meeting Transcription Tools (2026)
A research-backed roundup for firms that cannot send client audio to vendor cloud.
⚡ Protect Your Client Communications Now
Don't risk your client data. Deploy a truly private, SEC & FINRA-compliant solution with complete data sovereignty today.
✅ SEC Compliant · ✅ FINRA Ready · ✅ Your Infrastructure · ✅ Full Customization
Why Choose Meetily for Enterprise?
Complete Data Sovereignty
Self-hosted deployment with 100% local processing. Your meeting data never leaves your infrastructure. Full compliance with GDPR, HIPAA, and other regulations.
You Manage, We Provide
You manage your users and deployment. We provide the software and licenses - no cloud dependency, no vendor lock-in.
Priority Support
Dedicated support team, direct access to engineers, custom integration assistance, and priority bug fixes. White-glove deployment available.
Flexible Licensing
Volume pricing, annual billing options, and custom licensing to fit your organization's needs. Scale as your team grows.
Have questions? or join our GitHub community